Critical Citrix vulnerabilities under attack
Citrix has warned about critical vulnerabilities in its NetScaler products. Attackers are already exploiting these flaws, posing a serious risk to users.
Citrix has issued a warning regarding eight critical vulnerabilities in its NetScaler products, with two of them, CVE-2026-88771 and CVE-2026-88772, scoring 9.5 on the CVSS scale. The first allows for remote code execution, meaning an unauthenticated attacker can execute arbitrary commands on the affected system. The second vulnerability is a memory overflow that could lead to remote code execution or even denial of service.
## Why it matters These vulnerabilities are particularly concerning because they enable attackers to gain control of critical systems without requiring authentication. This could result in data loss, service interruptions, and significant damage to the reputation of businesses using these products.
## What we know Citrix has confirmed that these vulnerabilities are already being actively attacked. Additionally, a Reddit thread suggests that at least one Citrix channel partner was aware of these issues a day before the company made its public disclosure and advised users to take their NetScalers offline.
## What remains unclear It is still unclear the total extent of the attacks or how many organizations have been affected so far. The company has not provided details on the measures users can take to mitigate these risks while a solution is being worked on.
👉 Thinking of buying? Our guide helps you choose: Best WiFi Security Cameras for 2026.
Read at the original source:
The Register →Related news
 Security
Pentagon establishes covert tech sabotage agency
The Pentagon has set up a secret office aimed at disrupting foreign tech developments that threaten U.S. military superiority. Concerns arise regarding the oversight of these operations.
 Security
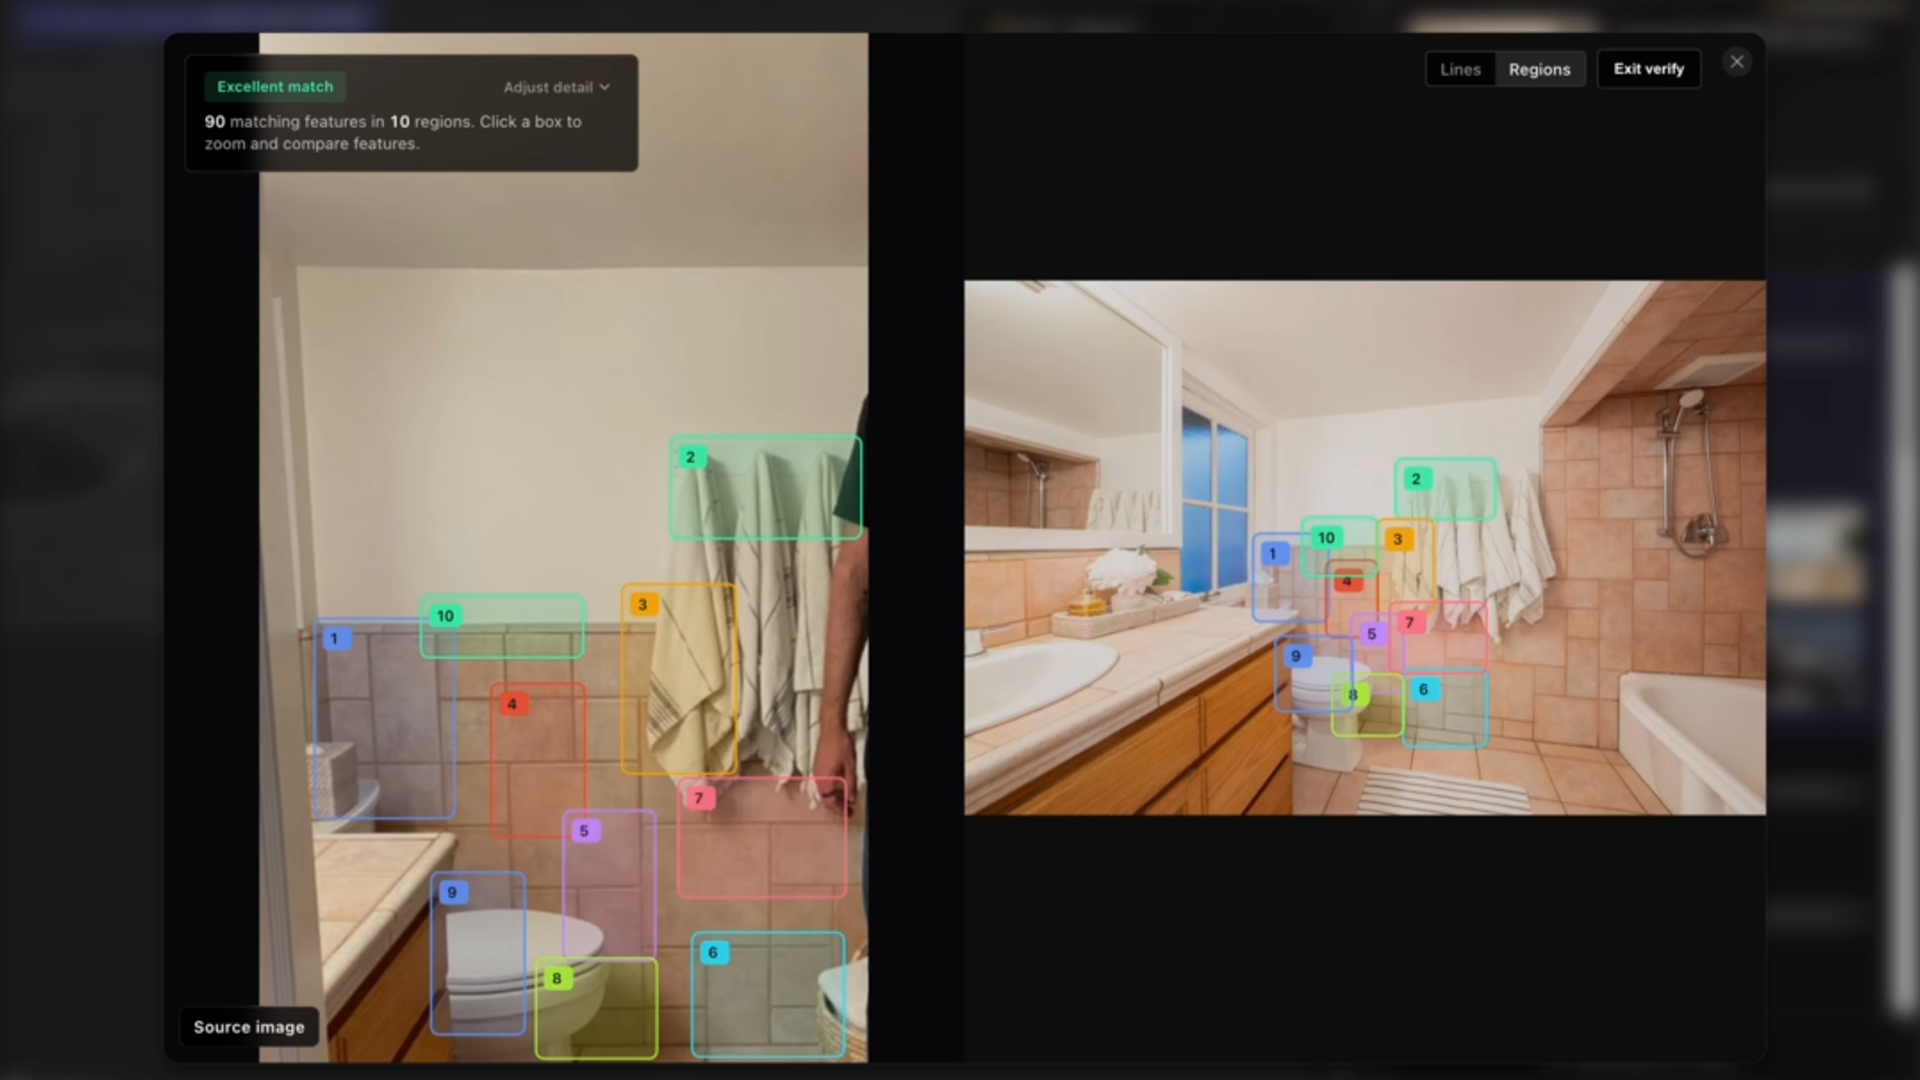
Raven: AI identifies locations from interior photos
Raven, an AI tool, can locate properties using interior photos. This advancement raises concerns about privacy and data usage.
 Security
US Government orders removal of all DeepSeek products
Federal agencies must remove DeepSeek due to security concerns.