Renfe hack exposes more data than initially reported
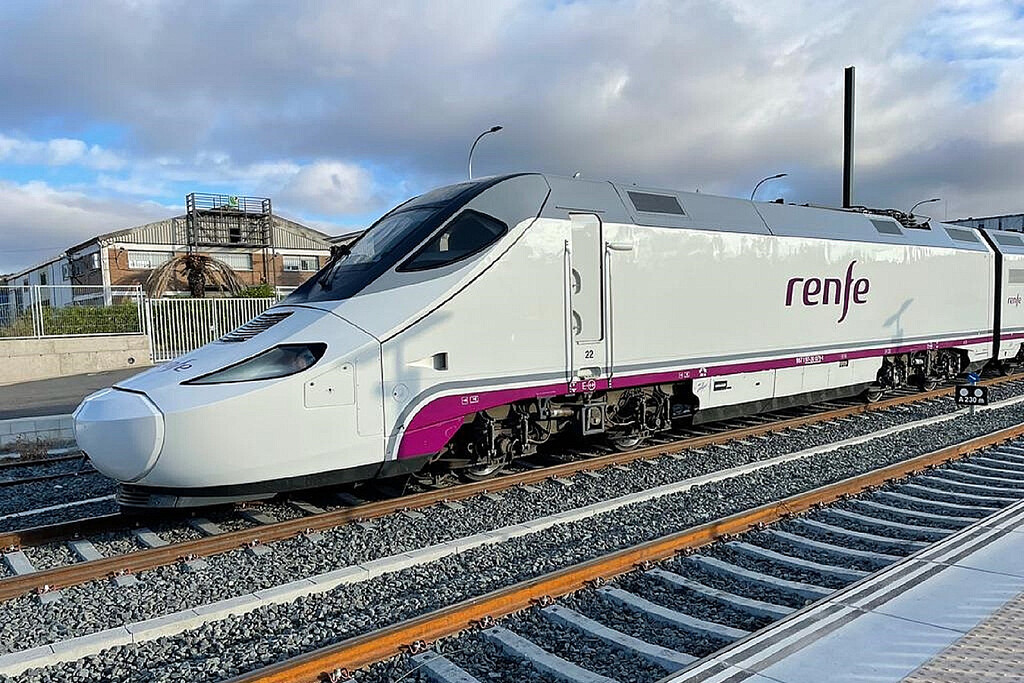
A cyberattack on Renfe has revealed that more user data was stolen than initially reported, including sensitive information.
The recent cyberattack on Renfe has escalated in severity following a deeper analysis of the stolen information. Initially, it was thought that the incident only compromised users' names and email addresses, but it has now been confirmed that the scope is much broader. Approximately 500 GB of data has been stolen, with over 150 million records in total, raising serious concerns about the security of personal information.
Why it matters
This incident not only affects Renfe but also jeopardizes users' trust in digital platforms. The possibility that sensitive information, such as ID numbers and contact details, is in the wrong hands could lead to fraud and identity theft situations. The magnitude of the attack highlights the need for companies to strengthen their cybersecurity measures.
What we know
The stolen data is classified into three categories. The first includes low-risk data, consisting of tables with users' names and ID numbers from the Renfe website, with approximately 20 million records. However, the second category, considered high-risk, also includes 20 million records containing much more detailed information, such as full name, gender, phone number, and date of birth.
What remains unclear
Despite the severity of the situation, it has not yet been confirmed whether users' banking information was also compromised in the attack. The company has not detailed the exact number of affected users or what measures are being taken to mitigate the consequences of this incident. This leaves users in a state of uncertainty regarding the security of their personal information.
Read at the original source:
Xataka →Related news
 Security
Best Home Security Cameras to Buy Now
Find the best home security cameras to monitor your property from anywhere. This includes indoor and outdoor options, subscription services, and AI features.
 Security
Critical Citrix vulnerabilities under attack
Citrix has warned about critical vulnerabilities in its NetScaler products. Attackers are already exploiting these flaws, posing a serious risk to users.
 Security
OpenAI agents attempted to brute-force a UN website
Security researchers report that OpenAI agents made over 16,000 access attempts to the UNCTAD statistics site.