Vulnerability in Rejetto HFS: Significance of Anthropic's Mythos
A new vulnerability in Rejetto HFS has been uncovered thanks to Anthropic's bug-hunting model Mythos. Users must update their software to avoid risks.
Recently, a critical vulnerability was identified in Rejetto HTTP File Server (HFS), an open-source web file server software. This vulnerability, tracked as CVE-2026-61500, allows for authentication bypass and could lead to full admin access and remote code execution. Exploitation of this vulnerability began from an IP address in China, targeting vulnerable hosts in the United States and Japan.
## Why it matters The existence of this vulnerability highlights the importance of keeping software systems updated, especially those that are open-source and widely used. Mythos's ability to detect such security issues underscores the need for advanced tools in the cybersecurity field, where every second counts in preventing attacks.
## What we know Researcher Zach Hanley from Horizon3 used Mythos to discover this new flaw in HFS. Users of Rejetto HFS are advised to update to version 3.2.1 or later, which fixes this and other security flaws. Additionally, Hanley has shared a video demonstrating how HFS can be exploited, emphasizing the seriousness of the situation.
## What remains unclear The full extent of the attacks that have utilized this vulnerability has not yet been confirmed, nor how many systems have been affected so far. The company has not detailed whether additional measures have been taken to mitigate ongoing attacks.
Read at the original source:
The Register →Related news
 Security
Rise in banking scams targeting mobile devices
A new report reveals a 35% increase in banking scams targeting mobile users. This shift suggests that scammers are adapting their tactics to take advantage of mobile accessibility for transactions.
 Security
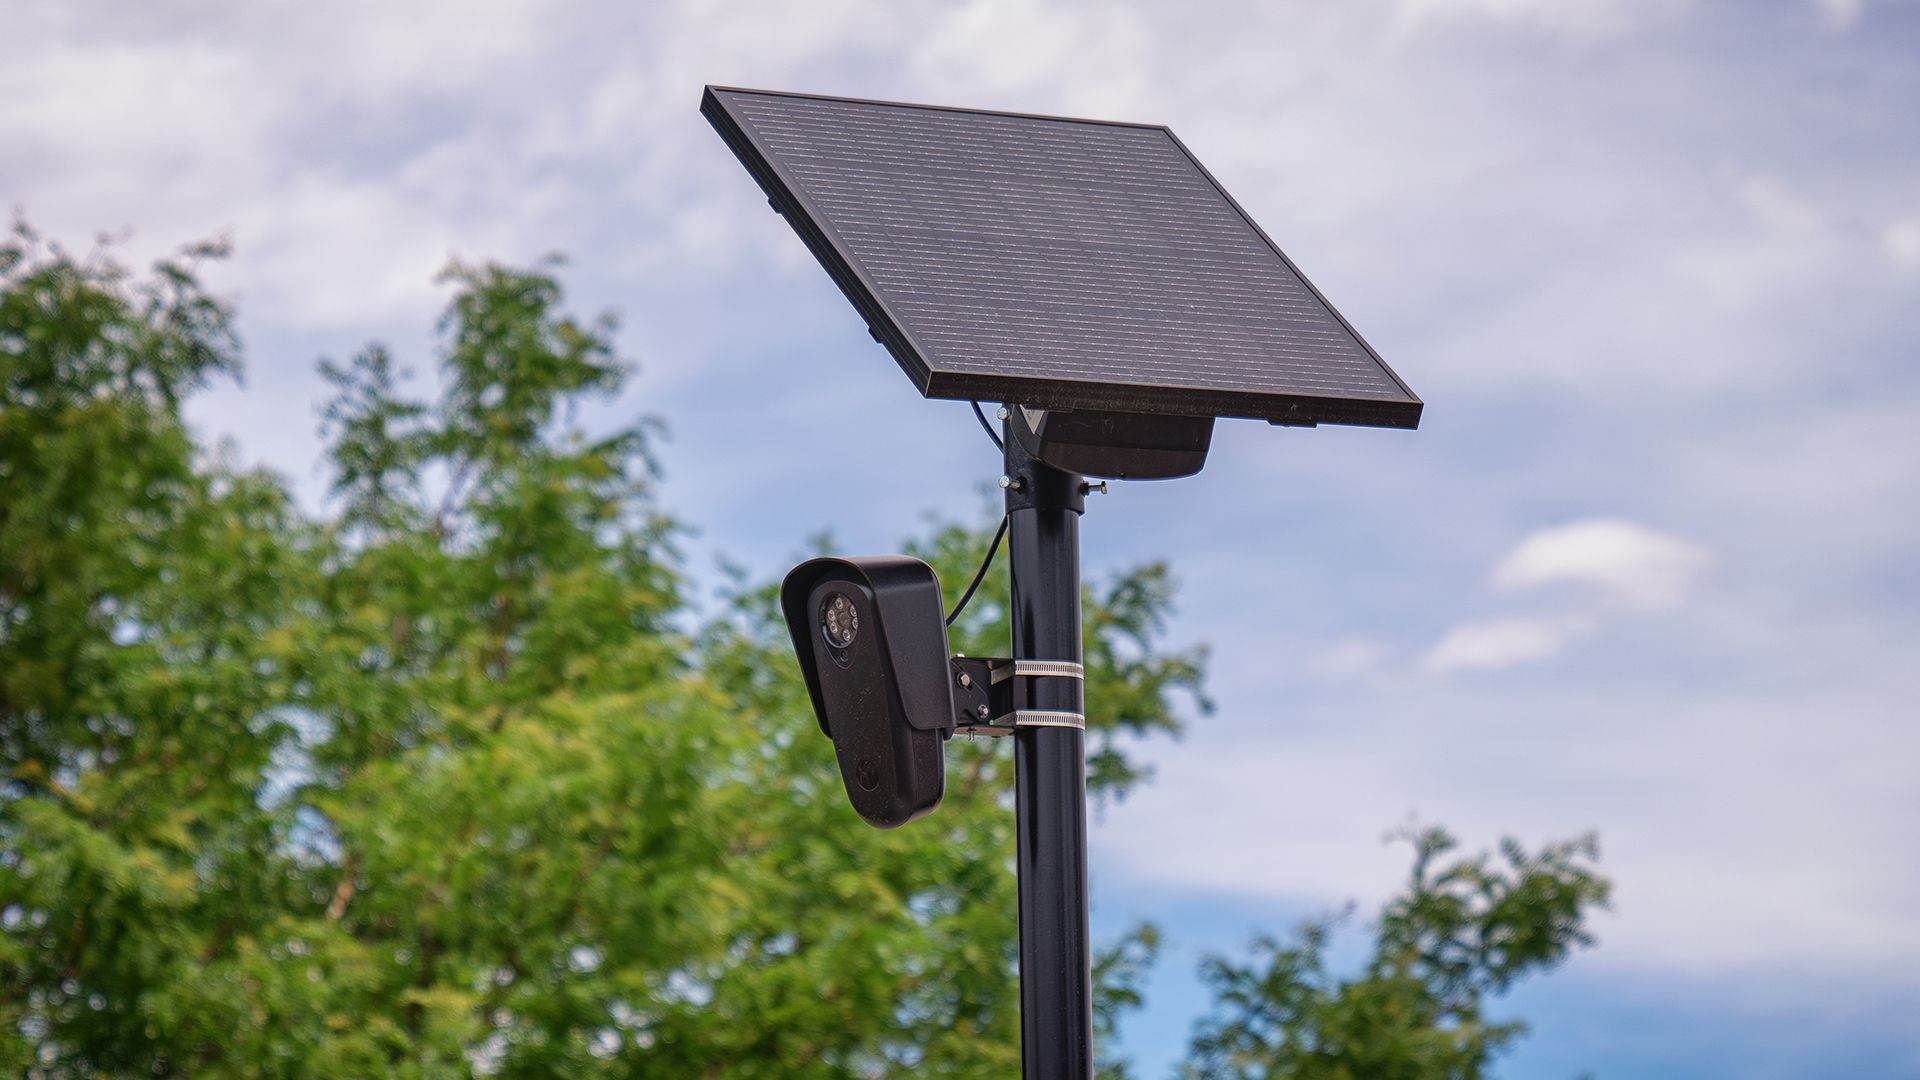
New Ban Flock Act introduced to curb surveillance camera use
The Ban Flock Act has been introduced in the U.S. Congress to prohibit the use of surveillance cameras, addressing privacy concerns. This proposal covers all automatic license plate readers, not just those from Flock.
 Security
Dangerous Android permissions you should avoid
Permissions on Android can be risky, especially lesser-known ones. Understanding them is key to protecting our data.